Cybersecurity for Industrial Web Services
Cybersecurity Built Into Industrial Web Services
Your website helps buyers find products, submit RFQs, and do business with your company. Security belongs in the decisions behind those services: who can sign in, where information goes, how systems connect, and how they recover.
TotalWeb Partners brings that security focus to industrial websites and business applications under the technical leadership of Gavin Siver, our Chief Technology Officer and an ISC2 Certified Information Systems Security Professional (CISSP®).
A Security Foundation for the Way Manufacturers Work
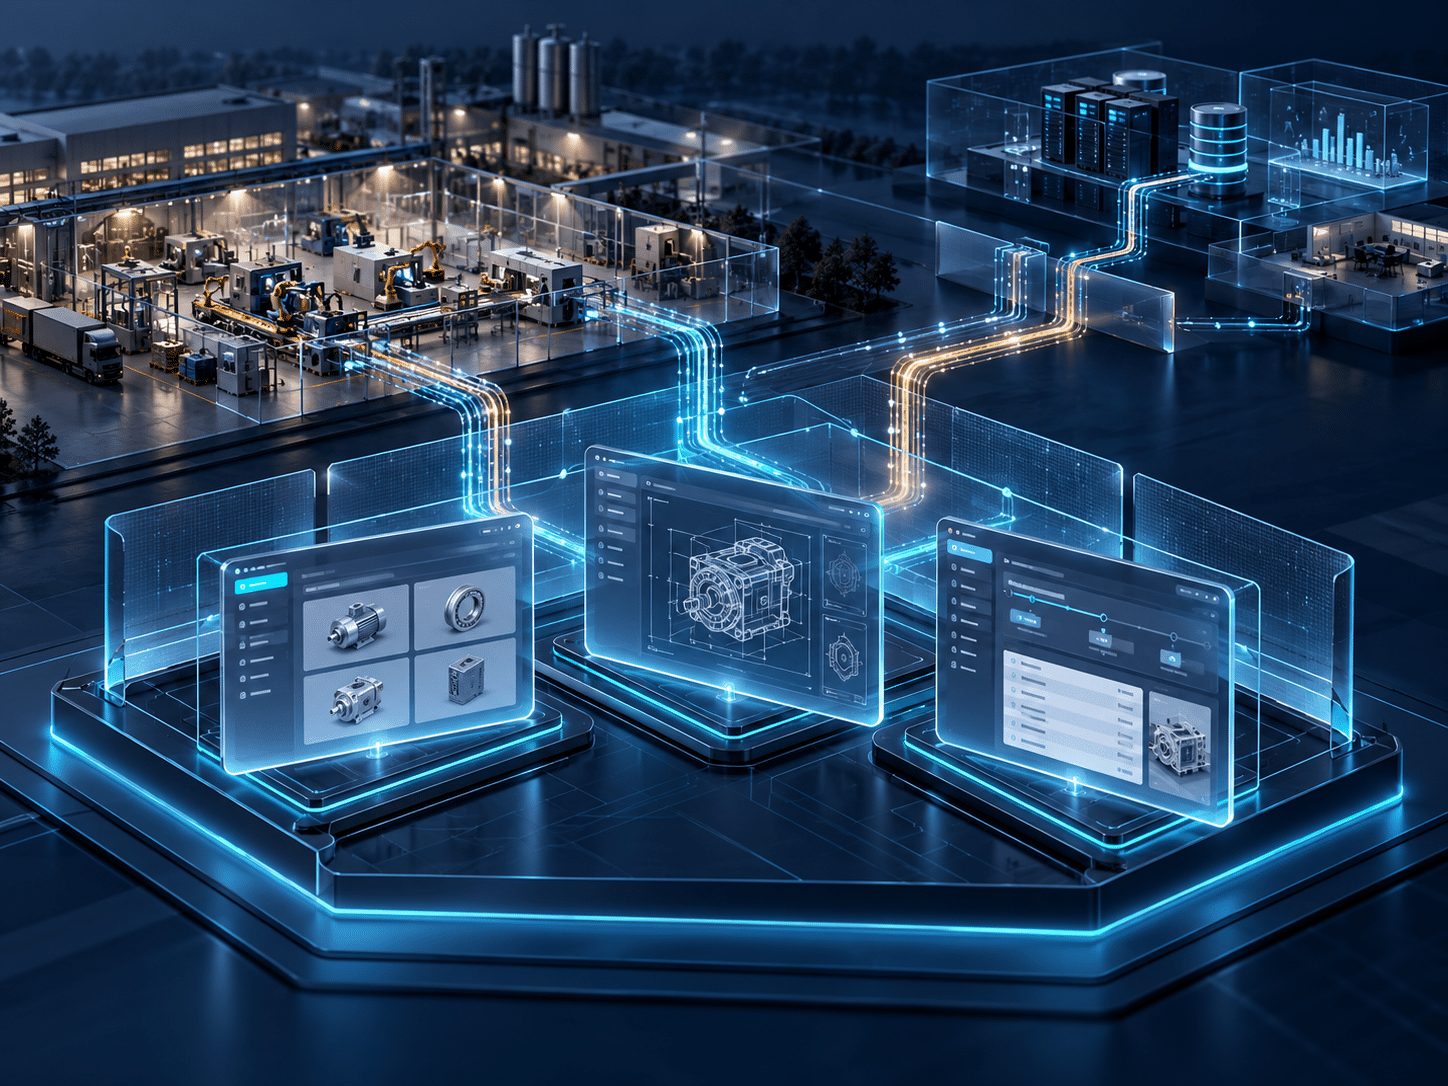
Industrial web services can include searchable catalogs, private customer pricing, employee logins, quote requests, and connections to business systems. Each connection creates decisions about access and data handling.
Our approach starts with the workflow. What information should a visitor see? What belongs behind a login? Who should receive an uploaded drawing? Does an integration need permission to read information, change it, or both? Those questions help shape the application before it becomes part of daily operations.
That approach connects with TWP’s industrial web design and online marketing services, with security considered alongside the buying experience and ongoing support.
CISSP Leadership, Backed by Hands-On Industrial Experience
ISC2 describes CISSP as a gold-standard information security certification. The credential recognizes broad security knowledge and experience across risk management, architecture, access control, operations, and software development. Gavin’s certification adds a recognized credential to his work designing and operating customer systems.
His experience includes developing a multi-site industrial inventory and procurement platform tracking hundreds of millions of dollars in inventory. His responsibilities span software engineering, infrastructure, and cybersecurity, including security and traffic controls across 150 corporate customers.
As his bio explains, he applies “defense in depth to protect access and data integrity.” That means using safeguards at several layers, including multi-factor authentication, role-based permissions, and controls at the application, database, and network levels.