Manufacturing Cybersecurity Review
Find the Gaps Between Your Website, Office, and Plant
Who can reach your plant systems, engineering files, and customer information? Review the access paths across your website, office, and facility networks, then give your team a prioritized plan for what to address first.
TotalWeb Partners’ Manufacturing Cybersecurity Review is a defined diagnostic engagement under CISSP-certified CTO oversight. We examine agreed systems and available evidence, then give your leadership and IT teams a prioritized plan for reducing risk.
Scope and pricing are defined before work begins, based on your facilities, systems, and review requirements.
A Practical Review for Industrial Operations
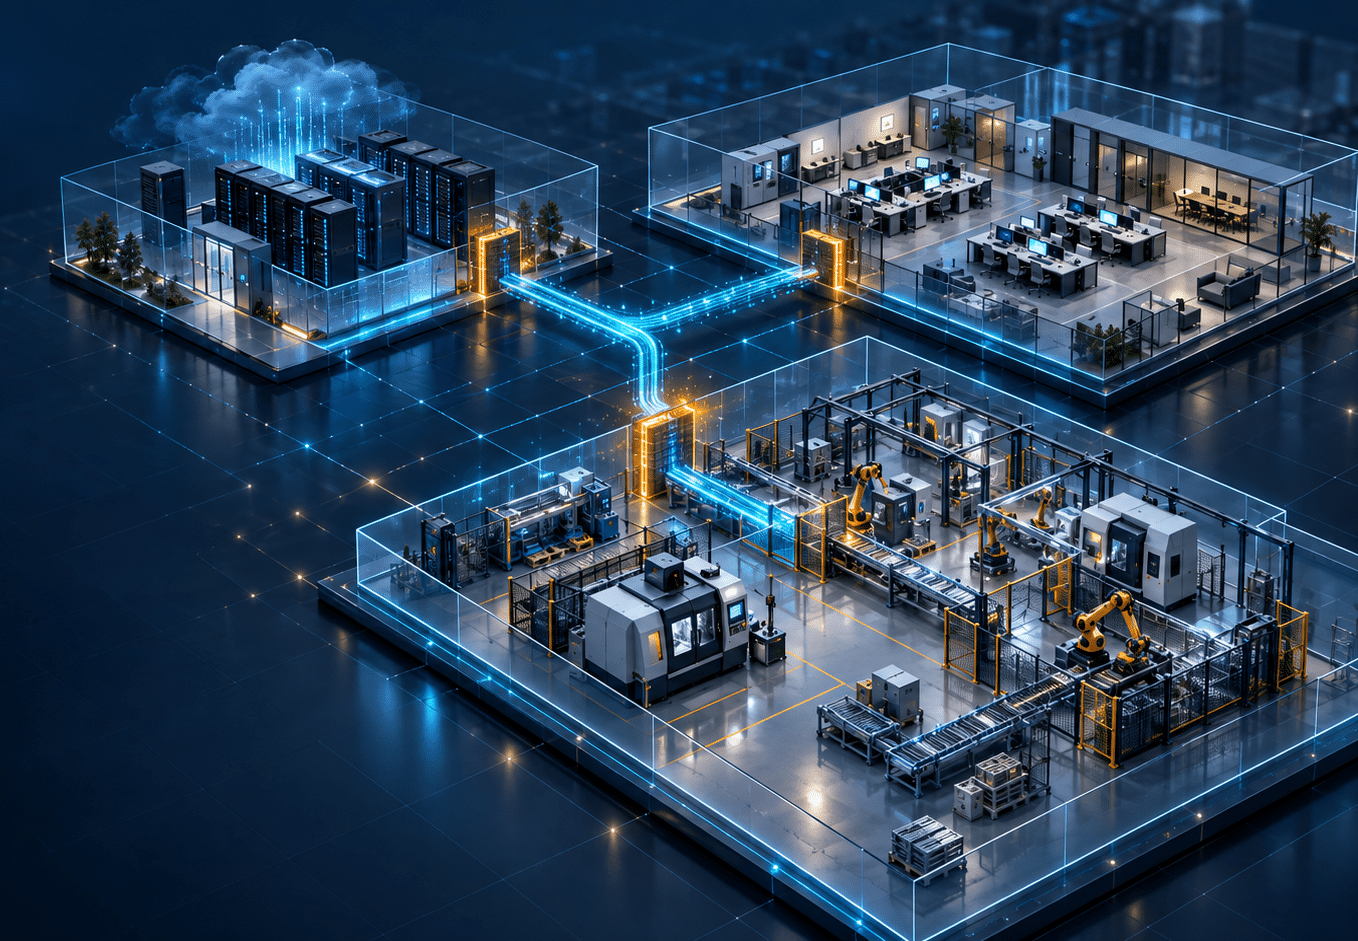
This review is for manufacturers, fabricators, machine shops, and industrial suppliers that need a clearer view of cyber exposure. It connects web and application security with business concerns: protecting drawings and customer information, limiting unauthorized access, and understanding recovery dependencies.
TWP’s industrial work includes websites, catalogs, RFQ workflows, and business applications. Our CTO, Gavin Siver, holds the CISSP® credential and has developed multi-site industrial inventory and procurement software.
Baseline Cyber & Web Risk Review for Manufacturers
A defined scope, CISSP oversight, documented findings, and a 30-day action plan. Your proposal specifies the number of facilities, domains, public IPs, applications, and network boundaries included, along with the delivery schedule and fee. This cybersecurity engagement is separate from TWP’s free web presence audit.
What We Review
The engagement defines the assets and evidence included in each area. We distinguish confirmed findings from gaps that need further validation.
External Exposure, Domains, and Email
Review agreed domains, public IP addresses, DNS, TLS configuration, and email authentication records such as SPF, DKIM, and DMARC. Identify exposed services and configuration concerns. Any external vulnerability scanning is limited to authorized assets and agreed methods.
Engagement Deliverables & Review Methodology
Clear, documented findings paired with an authorized and collaborative technical review process.
What You Receive
Comprehensive documentation and actionable roadmaps delivered upon completion.
How the Review Works
A structured, authorized technical review process that respects operational boundaries.
1. Agree on the Scope
Identify facilities, public assets, applications, network boundaries, and business priorities. Confirm permissions, evidence access, methods, exclusions, and the people responsible for production systems.
2. Review Evidence and Configurations
Work with your team on documentation, interviews, and configuration evidence. Use guided reviews or appropriately limited access agreed with the system owner. Perform only the technical checks authorized for the engagement. Identify evidence gaps explicitly rather than treating an unreviewed system as secure.
3. Turn Findings Into Next Steps
Discuss the results, assign proposed owners, and separate immediate improvements from work needing specialist support or additional testing.
Built Around Production Safety
Plant systems have operating and safety constraints that differ from office IT. The baseline review uses documentation and configuration evidence for plant boundaries. Active scanning, exploitation, control changes, and live recovery testing on production OT require a separate scope, plant-owner approval, and an agreed operating window.
The review is a point-in-time assessment. It does not certify compliance, guarantee protection, or replace a penetration test, continuous monitoring, or an incident-response service. Remediation implementation is separately scoped.
Put Your Next Security Decision on Firmer Ground
Tell us your company website, number of facilities, and the concern you want to address. We will define the right scope and provide pricing before work begins.
Please use the initial inquiry for business contact details and a short description. We will arrange an appropriate way to exchange system documentation.
Common Questions
We can discuss a review alongside your current web provider, IT team, and equipment vendors. The scope defines which systems and evidence are included and where specialist OT support is needed.
Documentation and configuration reviews can identify gaps and questionable access paths. Demonstrating that boundaries work may require separately authorized validation. The report states which conclusions the evidence supports.
The baseline engagement identifies and prioritizes findings. Configuration changes, remediation, retesting, and recurring support are separately scoped so your team can approve the work and its operational impact.
The findings can help organize evidence and remediation priorities. Your customer, insurer, or assessor determines its own requirements; the review does not guarantee acceptance.